AI Web Engineering vs Slow Digital Transformation: What Businesses Need to Fix Before Implementation
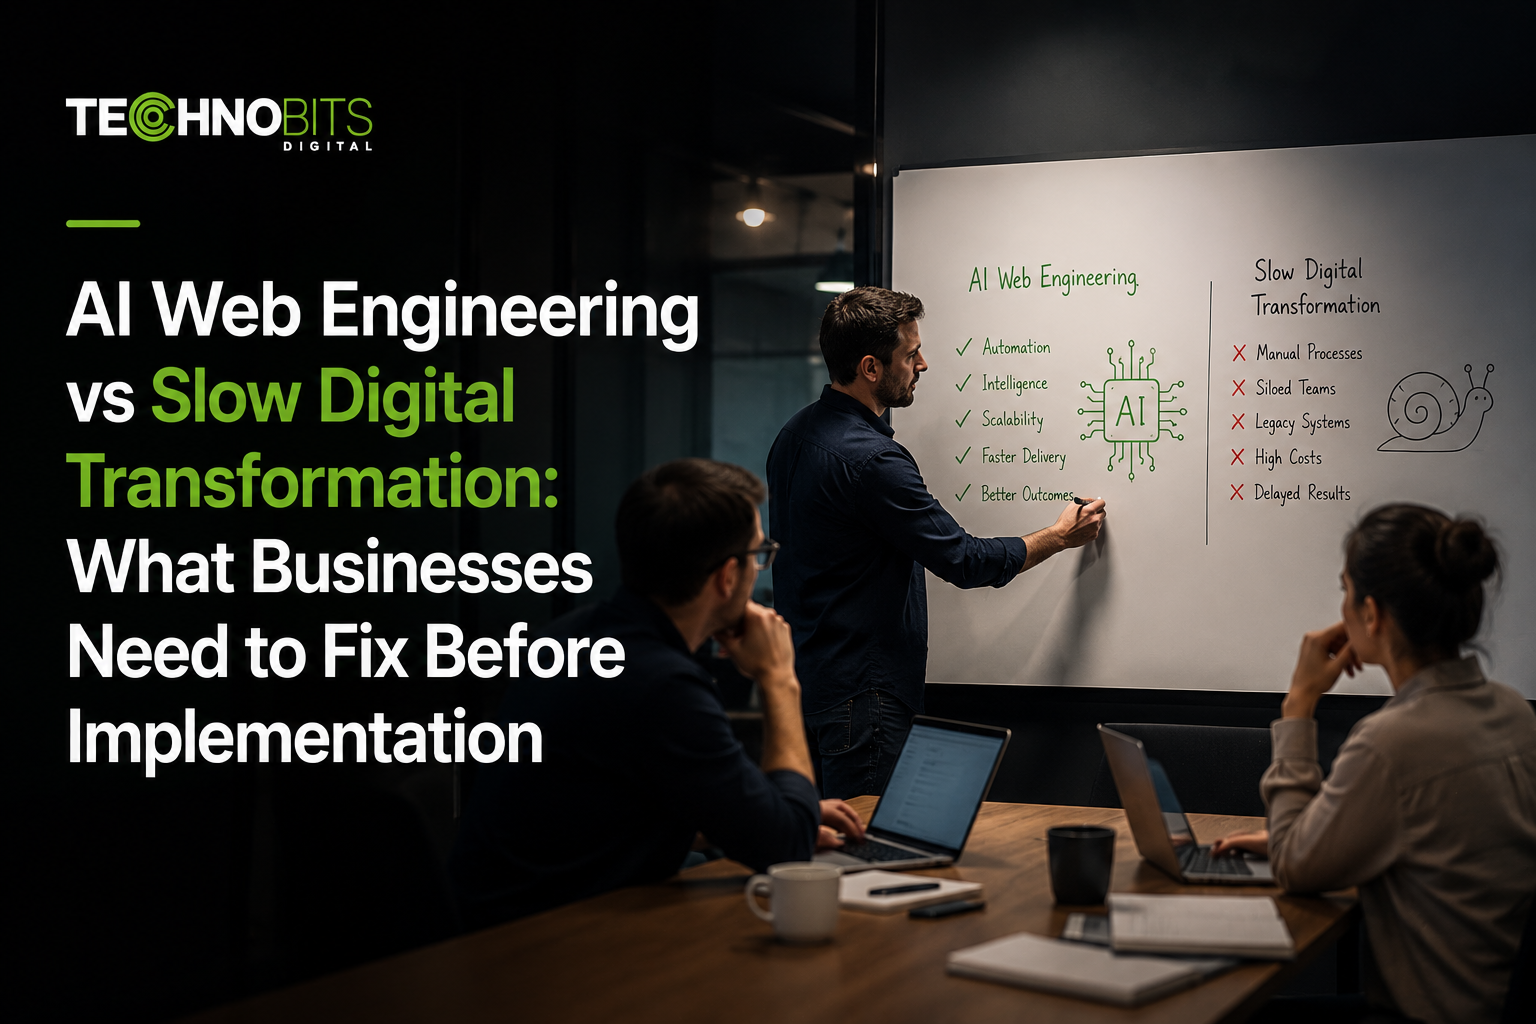
AI can accelerate interface production, code generation, test creation, and content operations, but it cannot compensate for unclear ownership, fragmented data, or a release process that still depends on manual approvals. For founders and technology leaders, the central risk is mistaking faster web development for faster organizational change. A team may ship new components quickly while customer records remain duplicated, integrations fail unpredictably, and operational staff continue moving information between spreadsheets.
Effective AI Web Engineering for gradual digital transformation begins with the systems surrounding the website, not solely the AI tool selected by the development team. Before implementation, evaluate the target user journey, application architecture, data quality, API readiness, security controls, deployment workflow, and operating model. AI-accelerated delivery can help reduce repetitive engineering work, but transformation only progresses when the resulting platform connects reliably with the people, processes, and systems responsible for running the business.
What Should Leaders Evaluate Before AI-Accelerated Web Engineering Begins?
Start by distinguishing the visible website from the complete digital service. A customer may arrive through search, compare an offer, submit information, create an account, make a payment, and request support. That seemingly simple journey can involve a content management system, identity provider, customer relationship platform, payment gateway, analytics stack, and internal fulfillment software. If those dependencies are not mapped, AI may generate an attractive front end that exposes the same delays and inconsistencies already present behind it. Requirements should therefore describe end-to-end transactions, system owners, data movements, exceptions, and recovery paths rather than only pages, features, and visual components.
Architecture readiness is the next concern. Determine whether the current website is a monolith, a conventional CMS, a headless platform, or a collection of services connected through APIs. Review supported runtime versions, dependency health, hosting constraints, deployment automation, and observability. An aging application with undocumented customizations may not be suitable for extensive AI-generated changes without prior remediation. Where editorial control is the primary requirement, structured CMS website development may be appropriate. Products with specialized workflows, permissions, or business rules may instead require an intelligent software architecture designed around those operational requirements.
You should also examine whether the organization can absorb a faster delivery cadence. AI tools can produce multiple implementation options in minutes, but product owners still need to prioritize them, engineers must review the output, and operational teams must prepare for changed processes. Useful readiness questions include:
Who owns each customer journey and has the authority to approve process changes?
Which system is authoritative for customer, product, plans, and consent data?
Can development, staging, and production environments be reproduced consistently?
Are acceptance criteria specific enough to validate AI-assisted code?
Who monitors integrations, incidents, and model-dependent functionality after release?
Can support teams explain and correct an automated decision when a customer questions it?
These questions expose whether the constraint is engineering capacity or organizational coordination. If ownership and operational controls remain unresolved, generating more software can increase the queue of unreviewed changes rather than shorten delivery.
Where AI Web Engineering Conceals Slow Transformation and Usually Goes Wrong
The first failure pattern is front-end acceleration without backend modernization. Code assistants can quickly create responsive layouts, form components, and API clients, yet they do not make an unstable legacy endpoint reliable. A new account portal may still depend on nightly data synchronization, manual identity checks, or a customer database that cannot represent current consent requirements. Users then encounter polished screens followed by delayed status updates, conflicting information, or support intervention. Before expanding the interface, document API contracts, latency expectations, error responses, retry behavior, and data ownership. Where systems cannot exchange information predictably, system integration services may be more important than generating additional interface code.
The second problem is treating generated output as coming soon software. AI coding tools may suggest deprecated libraries, insecure defaults, incomplete validation, or implementations that work only for the example included in the prompt. The output can appear plausible while mishandling authorization boundaries, concurrent updates, localization, accessibility, or unusual device behavior. Human review must assess architecture consistency, dependency risk, privacy implications, and maintainability. Automated tests should cover component behavior, API contracts, and critical user journeys, while manual exploratory testing examines conditions that predefined test cases may miss. A structured AI quality assurance workflow can support this process, but accountability remains with the engineering and product owners.
A third failure occurs when an organization automates an inefficient process without redesigning it. Consider a quotation workflow that passes through four departments because plans authority is unclear. Adding AI-generated summaries or automated emails may reduce typing, but it does not remove the approval bottleneck. The workflow should first be modeled as events, decisions, responsible roles, service expectations, and exception paths. Some steps may be eliminated; others may require explicit human judgment. This is particularly important when AI-generated content, recommendations, or classifications affect customers. The implementation needs confidence thresholds, escalation rules, audit records, and a defined fallback when the model or an external AI service is unavailable.
Which Architecture and Delivery Trade-Offs Should Shape the Decision?
The appropriate approach depends on the level of uncertainty in the product and the condition of the existing environment. A contained pilot can be useful when the business process is understood but the value of AI assistance remains uncertain. Examples include generating draft product descriptions for editorial review, classifying inbound inquiries, or helping developers create test fixtures. A platform-wide program is more appropriate only when shared identity, data, integration, and governance foundations are already credible. Starting small should not mean ignoring architecture; even a pilot needs boundaries for personal information, model access, logs, evaluation, and removal if the experiment is discontinued.
Decision area | Faster option | More controlled option | Question to resolve |
|---|---|---|---|
Application change | Extend the existing web stack | Separate services or staged replatforming | Can the current architecture support the expected transaction volume and change cadence? |
AI capability | Managed external model API | Model abstraction with routing and fallback controls | What data can leave the application boundary, and how dependent can the product become on one provider? |
Release strategy | Large feature launch | Feature flags and incremental exposure | Can the team observe failures and reverse a release without disrupting unrelated functions? |
Quality control | Generated unit tests | Layered automated and human testing | Which failures create material customer, operational, or security consequences? |
Content operation | Automated publishing | AI drafting with editorial approval | Which claims require evidence, brand review, or regulatory scrutiny? |
Buyers must also compare short-term delivery speed with long-term ownership. A generated application can accumulate duplicated components, inconsistent patterns, and unnecessary dependencies if prompts are handled as isolated tasks. Full-stack expertise matters because decisions made in the browser affect APIs, database transactions, caching, authentication, infrastructure costs, and monitoring. The team should define coding standards, approved libraries, architectural decision records, and review gates before output volume increases. Security analysis should include data flows, secrets management, role-based access, prompt injection exposure, and third-party service permissions. An IT security audit can help identify weaknesses, although remediation priorities still need to reflect the system’s actual risk profile.
Commercial evaluation should separate build effort from continuing operational cost. Model usage charges, observability, content review, regression testing, vendor changes, and support all remain after launch. The least expensive prototype may become costly if it cannot be tested, monitored, or transferred to another engineering team. Conversely, excessive abstraction can delay a modest use case that has limited risk. The decision should be proportional: stronger controls for customer-facing decisions and sensitive data, lighter controls for internal drafting or developer assistance, and explicit criteria for moving from experiment to production.
How Should Technobits Digital Structure Implementation Across the Full Stack?
Implementation should begin with discovery that produces technical artifacts rather than a broad aspiration to “add AI.” Technobits Digital can assess user journeys, application boundaries, integration dependencies, data sensitivity, and operational ownership before recommending a delivery path. The initial output may include a current-state system map, prioritized use cases, target architecture, risk register, and release plan. This approach helps separate work that genuinely benefits from AI acceleration from foundational work such as API remediation, identity consolidation, or database restructuring. It also allows business owners to decide whether the first investment should improve an existing service, modernize a platform component, or test a contained AI-assisted workflow.
A controlled implementation can follow a sequence such as:
Define the business event, user decision, or operational delay that the change must address.
Map every participating application, data source, external service, and responsible owner.
Classify information by sensitivity and decide what an AI provider may receive, retain, or process.
Choose an architecture that includes authentication, model access, validation, logging, and fallback behavior.
Build a thin end-to-end path before expanding interface coverage or automation volume.
Test normal, exceptional, adversarial, and unavailable-service conditions.
Release through controlled exposure, monitor behavior, and document operational ownership.
This sequence keeps AI-accelerated delivery connected to production engineering. Developers can use assistants for scaffolding, refactoring suggestions, documentation, and test generation, while reviewers verify every material change. Quality controls should include static analysis, dependency checks, integration tests, and browser or device coverage. For high-risk public applications, custom software testing can address specialized workflows that generic test suites do not represent. Security design may also require an AI cyber defense assessment covering model endpoints, malicious inputs, account abuse, and monitoring requirements.
Delivery governance must work across product, engineering, and operations, particularly when stakeholders or implementation teams operate from multiple offices. Technobits Digital can scope collaboration around common backlog definitions, environment access, code review rules, and handover records. This supports continuity while preserving accountability: one owner remains responsible for each release, incident, and architecture decision, regardless of where contributors are located.
What Do Business Owners Ask Before Approving AI Web Engineering?
Does AI-accelerated delivery automatically make transformation faster?
No. It can reduce time spent on code scaffolding, documentation, test preparation, and repetitive implementation, depending on the tool and review process. It does not resolve disputed requirements, poor data quality, delayed approvals, or unsupported legacy systems. Measure the complete lead time from business decision to stable production use, not only the time required to generate code. If review, integration, and release queues continue growing, the organization has accelerated production without improving flow.
Should we modernize the existing website or replace it?
The answer depends on maintainability, security support, integration capability, and the cost of incremental change. An existing platform may remain suitable if its dependencies are supported, its domain rules are understood, and it can expose reliable interfaces. Replacement becomes more credible when routine changes cause regressions, deployment is unsafe, or essential integrations cannot be added without extensive coupling. A staged migration can preserve working capabilities while selected domains move behind stable APIs.
How should AI-generated code be governed?
Apply the same engineering controls used for human-written code, with added scrutiny for provenance and hidden assumptions. Generated changes should enter version control, pass automated checks, receive peer review, and be traceable to a requirement. Teams should define which tools are approved, what source code or data may be submitted, and whether generated dependencies satisfy organizational policies. Sensitive credentials, production records, and proprietary code should not be placed into unapproved tools.
Which measurement shows whether transformation is improving?
Use operational measures tied to the selected journey: deployment frequency, change failure patterns, recovery time, API error rates, manual hand-offs, exception volume, and completion rates. Customer measures may include successful task completion, support escalation, and time to receive a confirmed outcome. AI-specific evaluation can examine factual accuracy, inappropriate responses, escalation frequency, and cost per processed task. No single metric proves success; the measurement set should connect engineering behavior with service reliability and business operations.
Planning AI-Assisted Web Modernisation?
Before adding AI to an existing web platform, identify whether the main constraint is frontend delivery, legacy architecture, fragmented data, unreliable integrations or an inefficient internal workflow.
Technobits Digital can help assess the relevant web development, software, integration, testing and security requirements based on your current platform and intended use case.